Added-line scanning
Only changed lines beginning with + are scanned. Context or deleted code does not generate the same finding.
03 / SOFTWARE ENGINEERING / DEVELOPER TOOLS
A tool for inspecting public GitHub pull requests and highlighting code changes that may deserve a closer review.
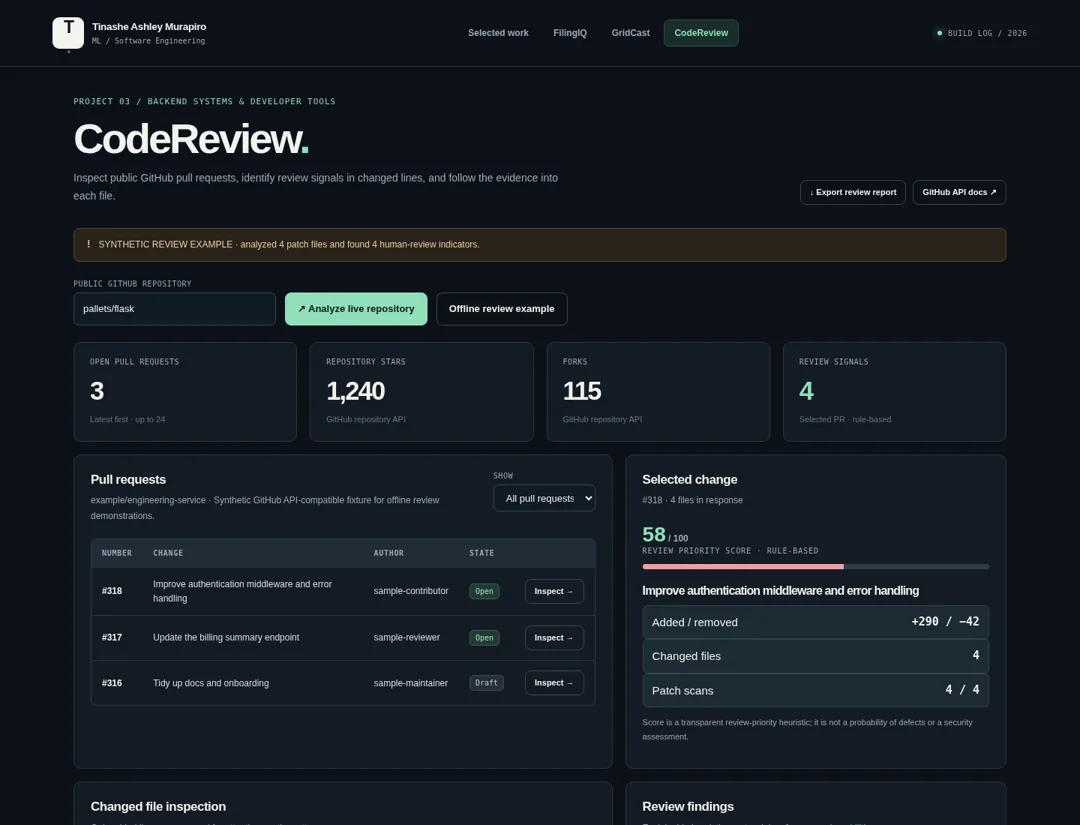 APPLICATION CAPTURE / LOCAL TESTING
01 / THE PROBLEM
Reviewing a pull request can mean scanning many files and diffs. A warning is more useful when it points to a specific change and explains why it may need attention.
The app retrieves public pull-request details and patches, checks added lines against a set of explicit patterns, and creates a checklist that points reviewers to the relevant files.
02 / FEATURES
Search public GitHub repositories and list open pull requests
Open a pull request and inspect modified files and change statistics
Run explainable rule-based checks on added patch lines
Flag risky patterns while explaining why human verification is required
Use a clearly identified synthetic example for offline testing and report exports
03 / IMPLEMENTATION
Only changed lines beginning with + are scanned. Context or deleted code does not generate the same finding.
When GitHub omits large patch fragments, the UI reports that coverage gap rather than assuming nothing suspicious exists.
Risk indicators are review prompts, not proof of a vulnerability, static-analysis certification, or trained AI judgments.
04 / TESTING & LIMITATIONS
The GitHub REST retrieval logic, patch-rule evaluator and browser interactions were locally tested. The bundled offline pull request is clearly synthetic and is not represented as public GitHub evidence.
Findings are heuristic and can be false positives or miss defects. GitHub API rate limits apply, and the host must permit outbound HTTPS. Do not use the score as a security certification.
05 / DATA SOURCES